Make your agent deployments audit-ready
Connect findings to the frameworks you use
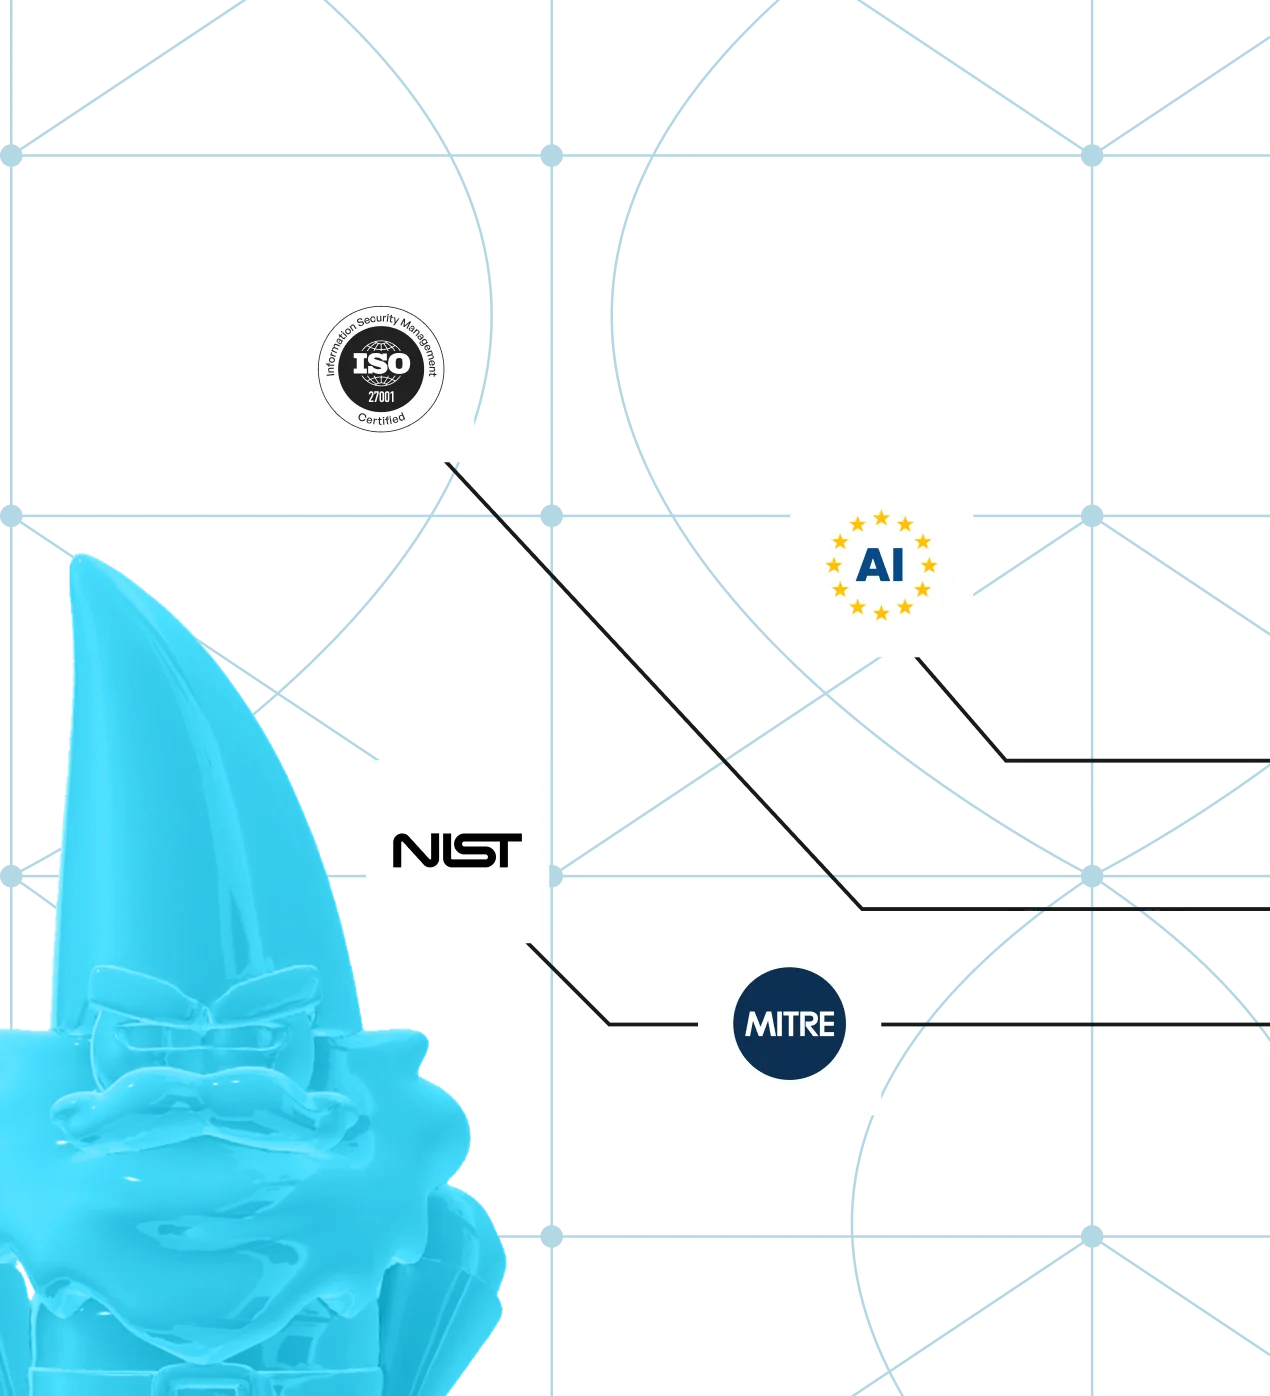
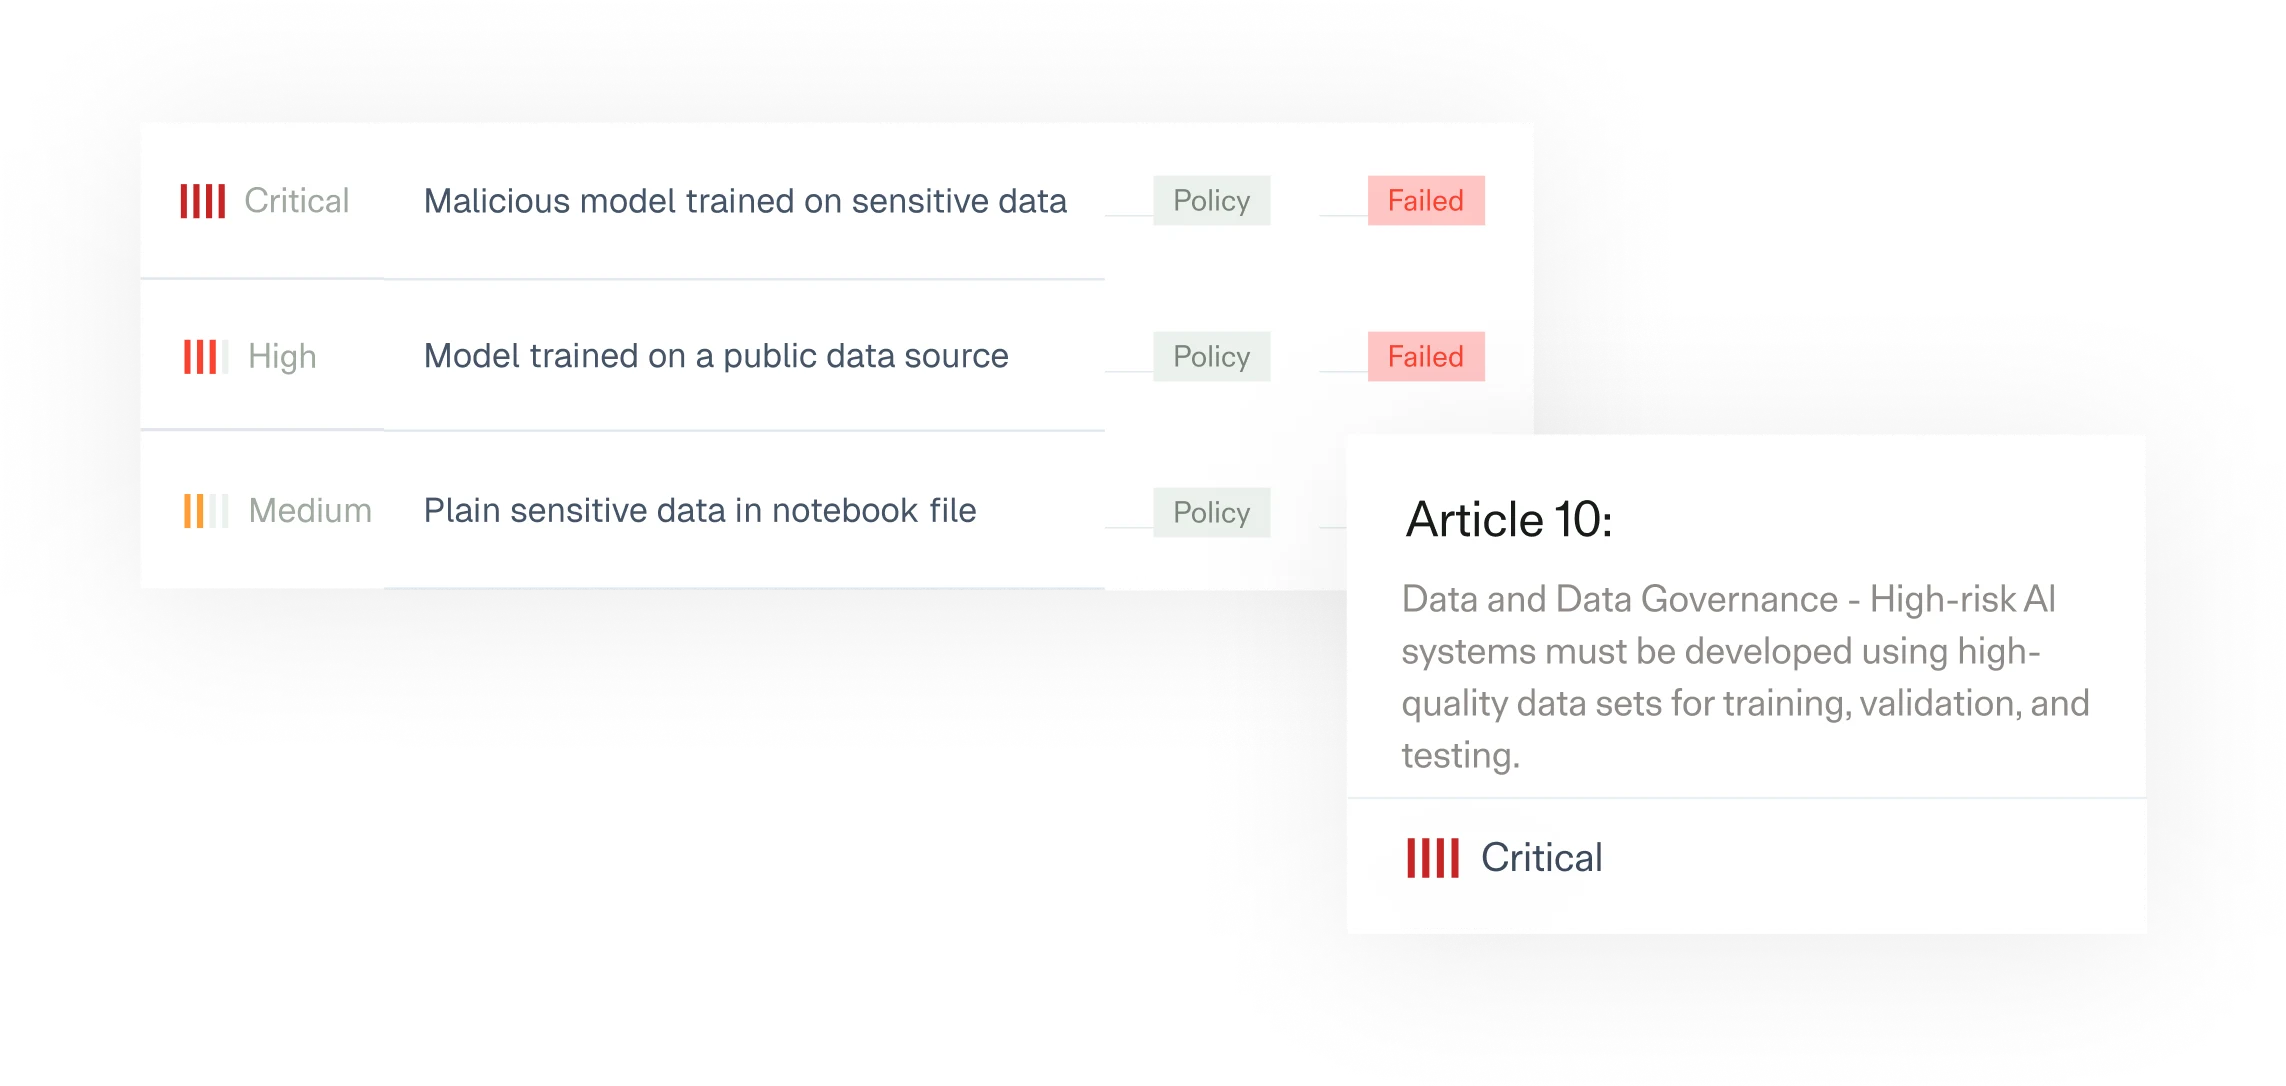
Noma maps findings to specific controls in the frameworks your organization needs to comply with: NIST AI RMF, EU AI Act, and ISO 42001 for regulatory compliance, and OWASP LLM Top 10 and MITRE ATLAS for industry benchmarks and security coverage.
Get an auditable AI inventory

Maintain a current record of agents, models, and connected tools across your organization. Give reviewers a clear view of the AI systems your governance program covers.
Show how agents perform in evaluations
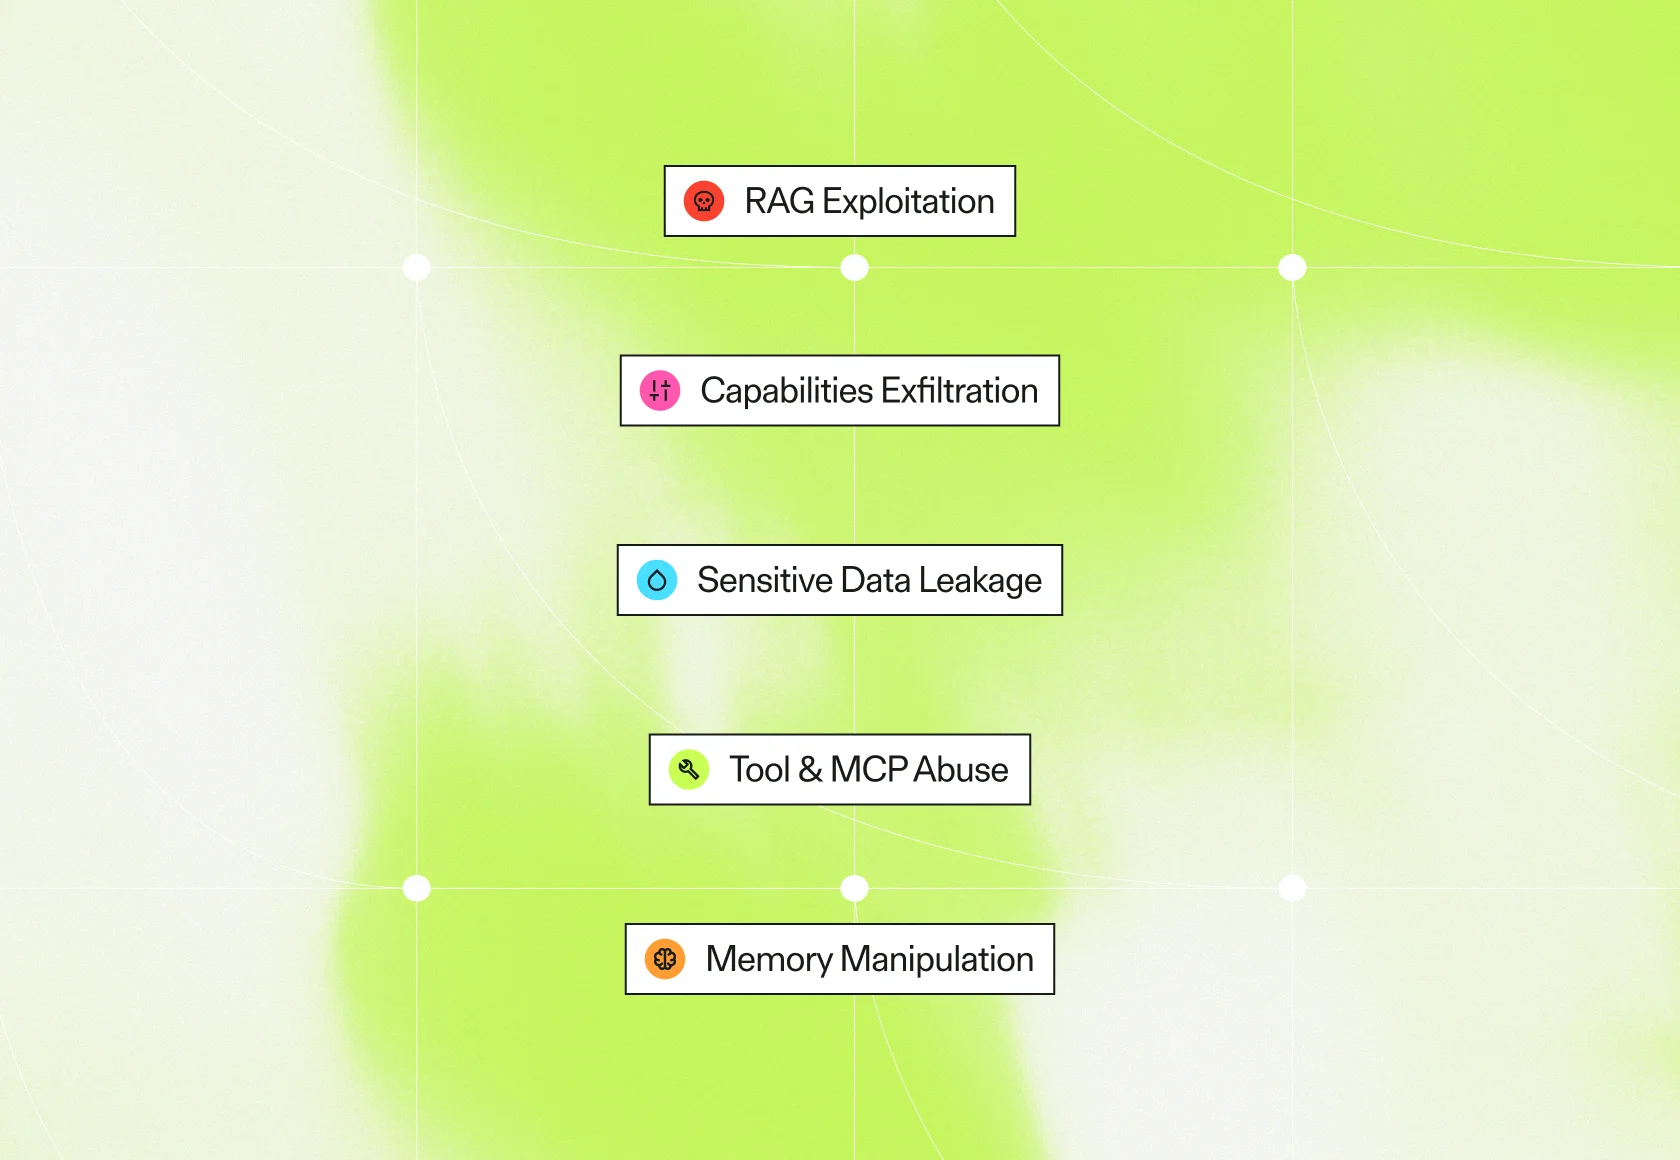
Use AI Red Teaming to assess security, privacy, and compliance risks across challenging scenarios. Bring test results into reviews to demonstrate resilience and identify where safeguards need improvement.
Prove that runtime controls are being enforced
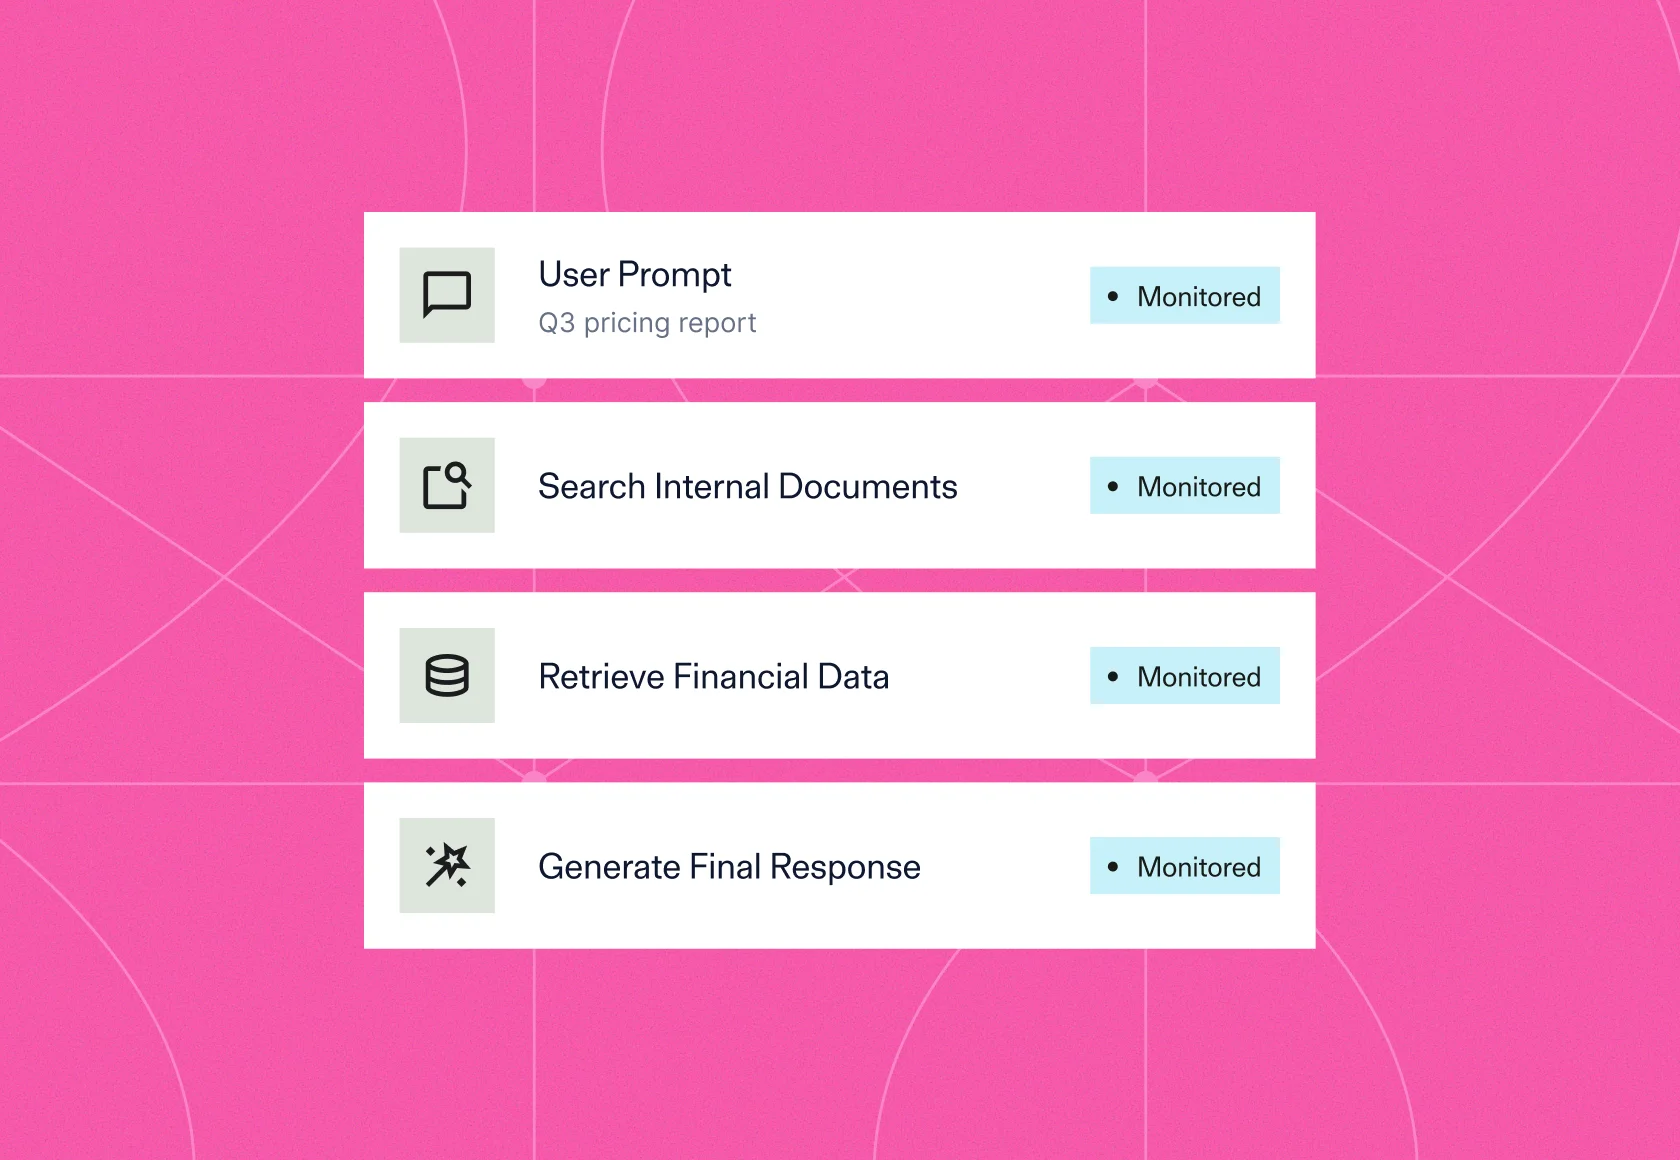
Review prompts, tool calls, detections, and enforcement actions together. Give auditors and security leaders evidence of how agents behaved and how your policies responded.
Staying current with regulations
Enterprise ready
Comprehensive coverage
With integrations with 80+ services and coverage spanning endpoint, SaaS, and cloud agents, Noma is the long-term enterprise partner for agent security and governance.
Enforce with your AI infrastructure
Decouple governance from any single control point and enforce policy through AI gateways, MCP gateways, agent hooks, agent SDKs, and direct APIs, using the infrastructure already in your environment.
Multiple deployment options
Support for both on-prem and SaaS deployments, so no model, training data, or security events leave your environment.
Built to Higher Standards.
FAQs
What AI regulations does Noma help with?

Noma maps findings and controls to the EU AI Act, NIST AI RMF, and ISO 42001, and to the OWASP LLM Top 10 and MITRE ATLAS security benchmarks, with framework-specific evidence for auditors.
What evidence does Noma produce for auditors?
A continuous AI asset inventory, framework control mappings with severity, adversarial test results, and runtime audit trails covering every prompt, tool call, and enforcement action.
Does Noma track regulatory changes?
Yes. Noma monitors regulatory developments and updates its compliance mappings, so teams stay current without chasing changes across NIST, ISO, and EU AI Act requirements.
Can Noma support ISO 42001 certification?
Yes. Noma's inventory, policy governance, testing evidence, and runtime audit trails map to ISO 42001 controls. Enterprise customers like UiPath use Noma's compliance capabilities to support their ISO 42001 certification.