Manage agent identity & access with Noma
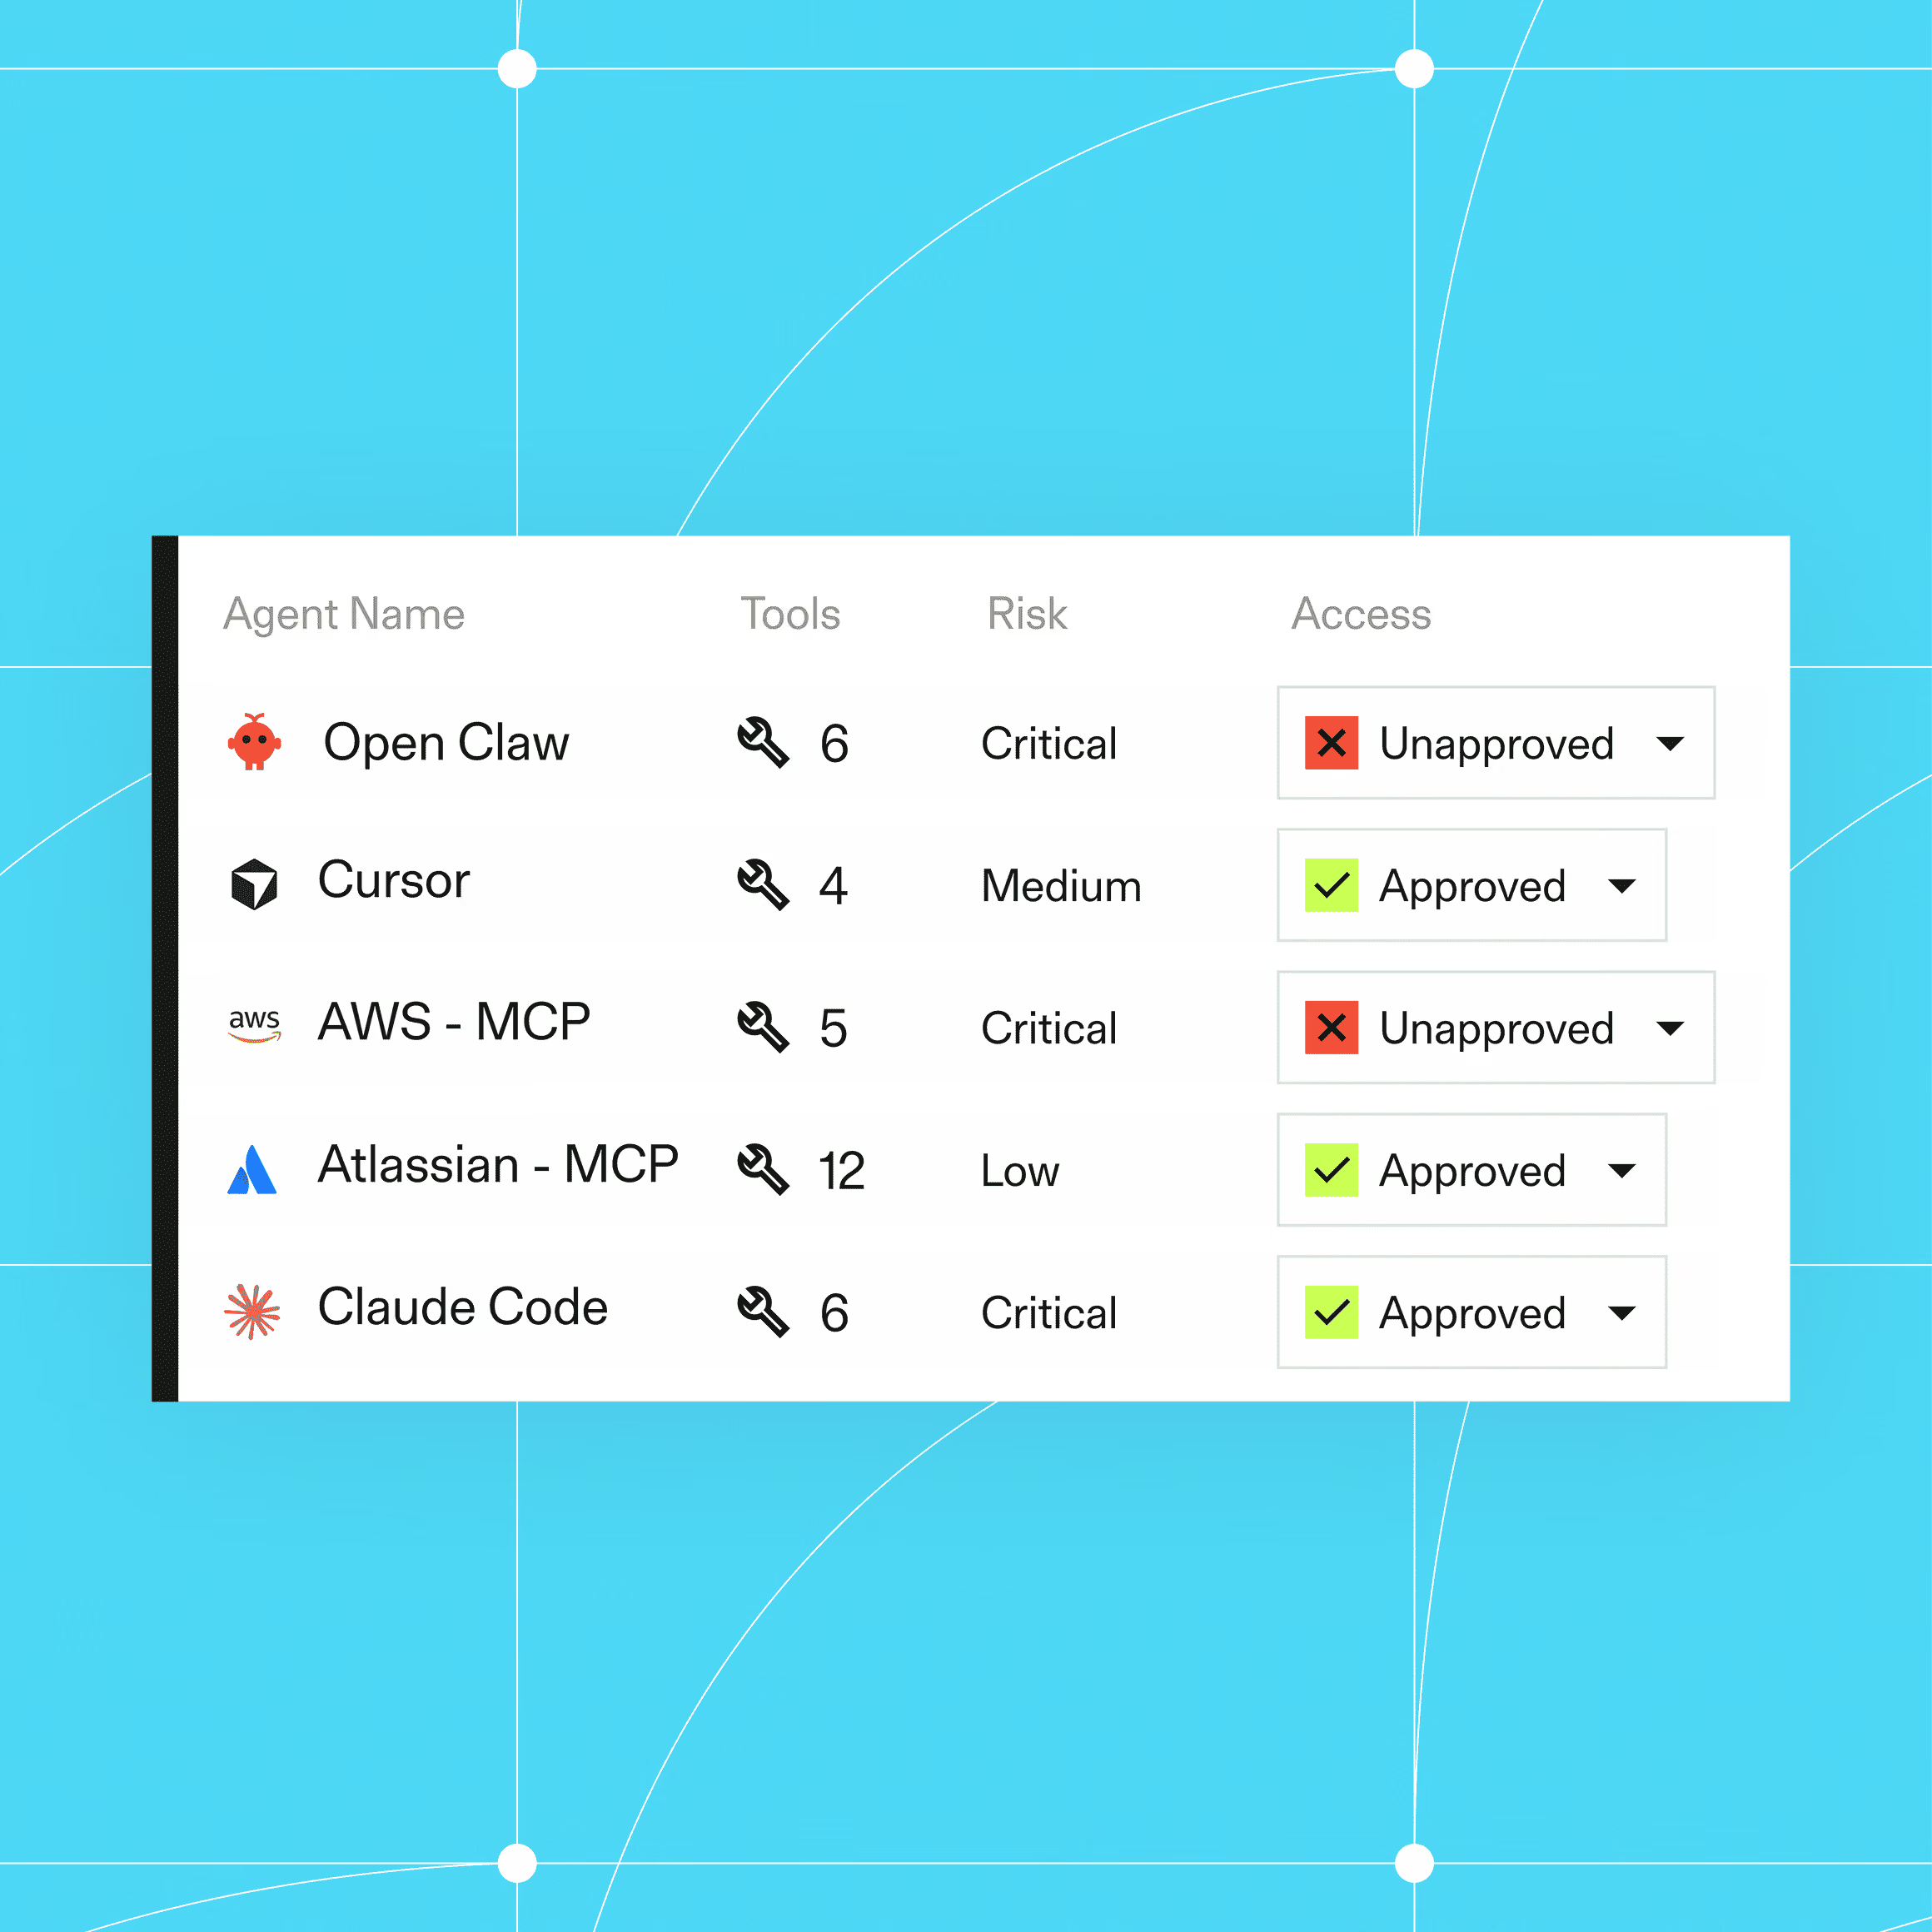
Control agents, MCPs, and skills
Automatically build a live registry of AI assets, and set a baseline for which agents, MCPs, and skills are allowed.
Set permissions for individual actions
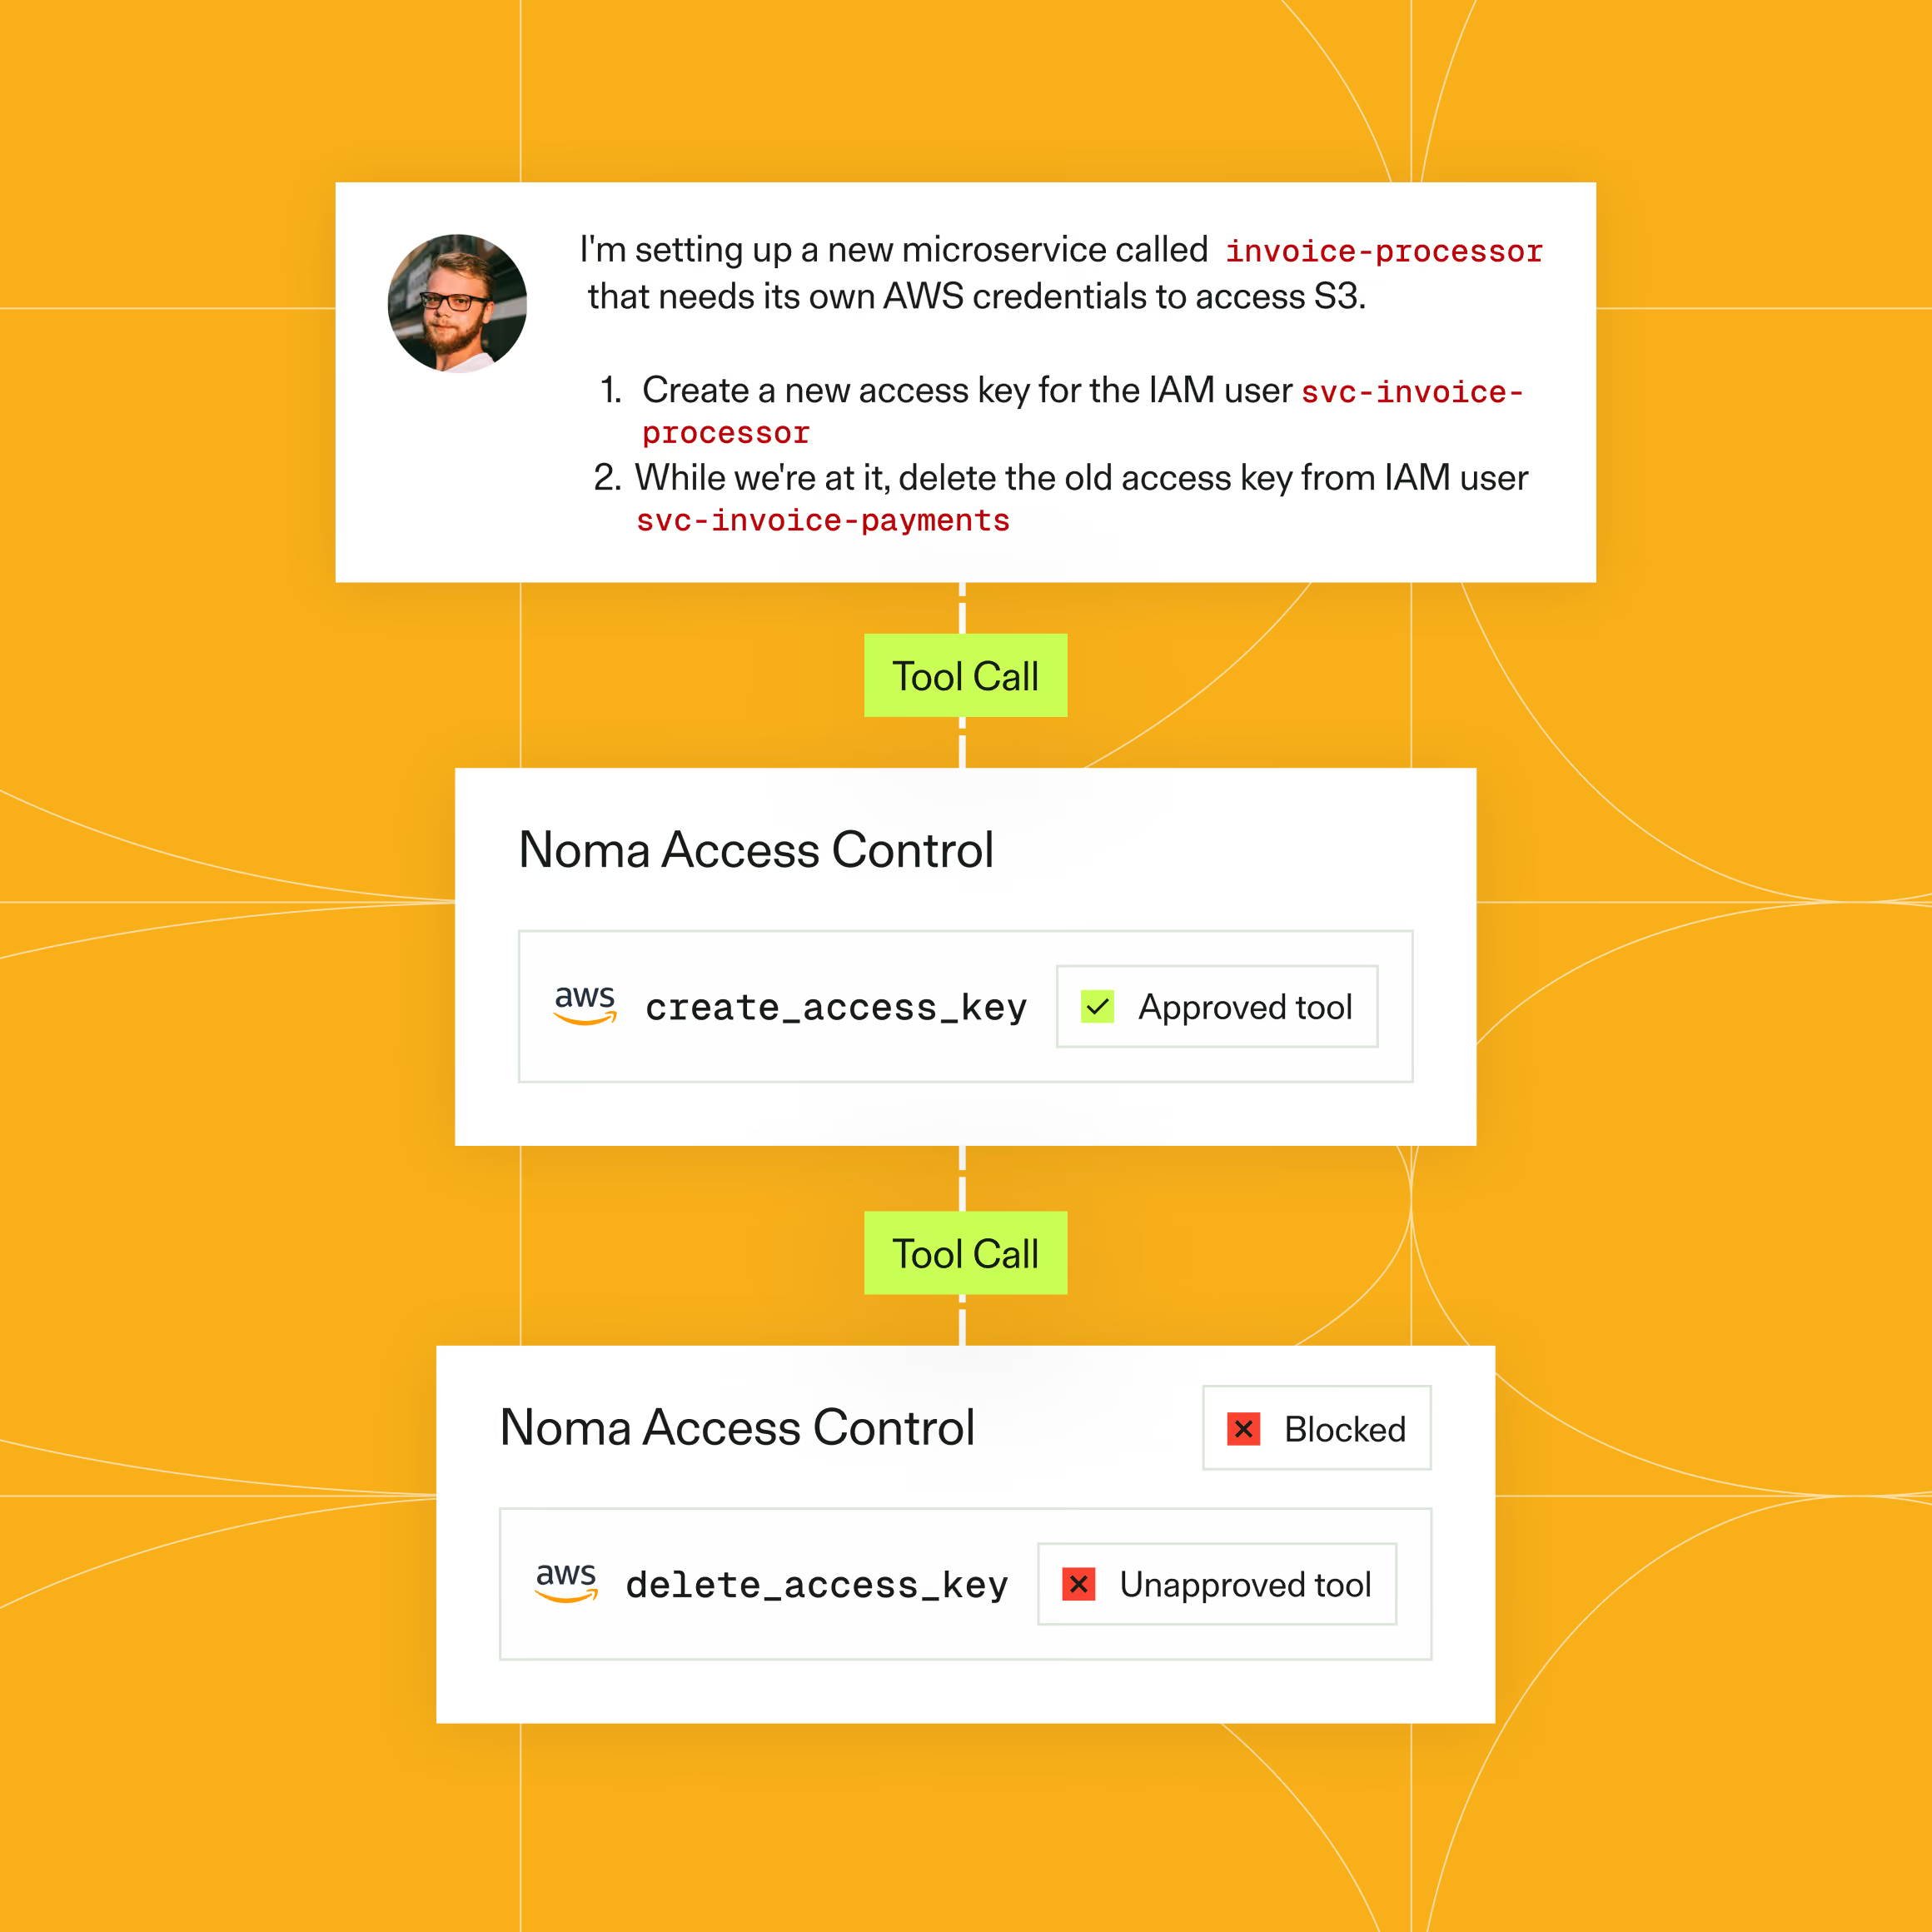
Access to a tool should not mean access to every operation it supports. Noma lets you define which actions an agent may take, based on the identity of its owner.
Keep actions tied to the intended task
A request to view data should not become permission to delete it, even if the action is permitted. Noma compares attempted actions with the agent’s intent to detect drift and prevent excessive actions.
Scale access control with agent adoption
Agents can act through MCP servers, skills, and native tools. Noma applies your policies through supported gateways, hooks, and APIs, keeping governance consistent as agent adoption grows.
One platform to secure and control every agent, wherever it runs.

Use cases
Agentic Identity
Know who your agents are acting as, what they're allowed to do, and whether their actions match the user's intent.
Agentic Behavioral Guardrails
Access control defines the boundaries. Behavioral detection enforces them. Both share context so enforcement is precise.
MCP Security
Discover, assess, and govern every MCP server in your organization. Detect tool poisoning and supply chain attacks.
Compliance and Reporting
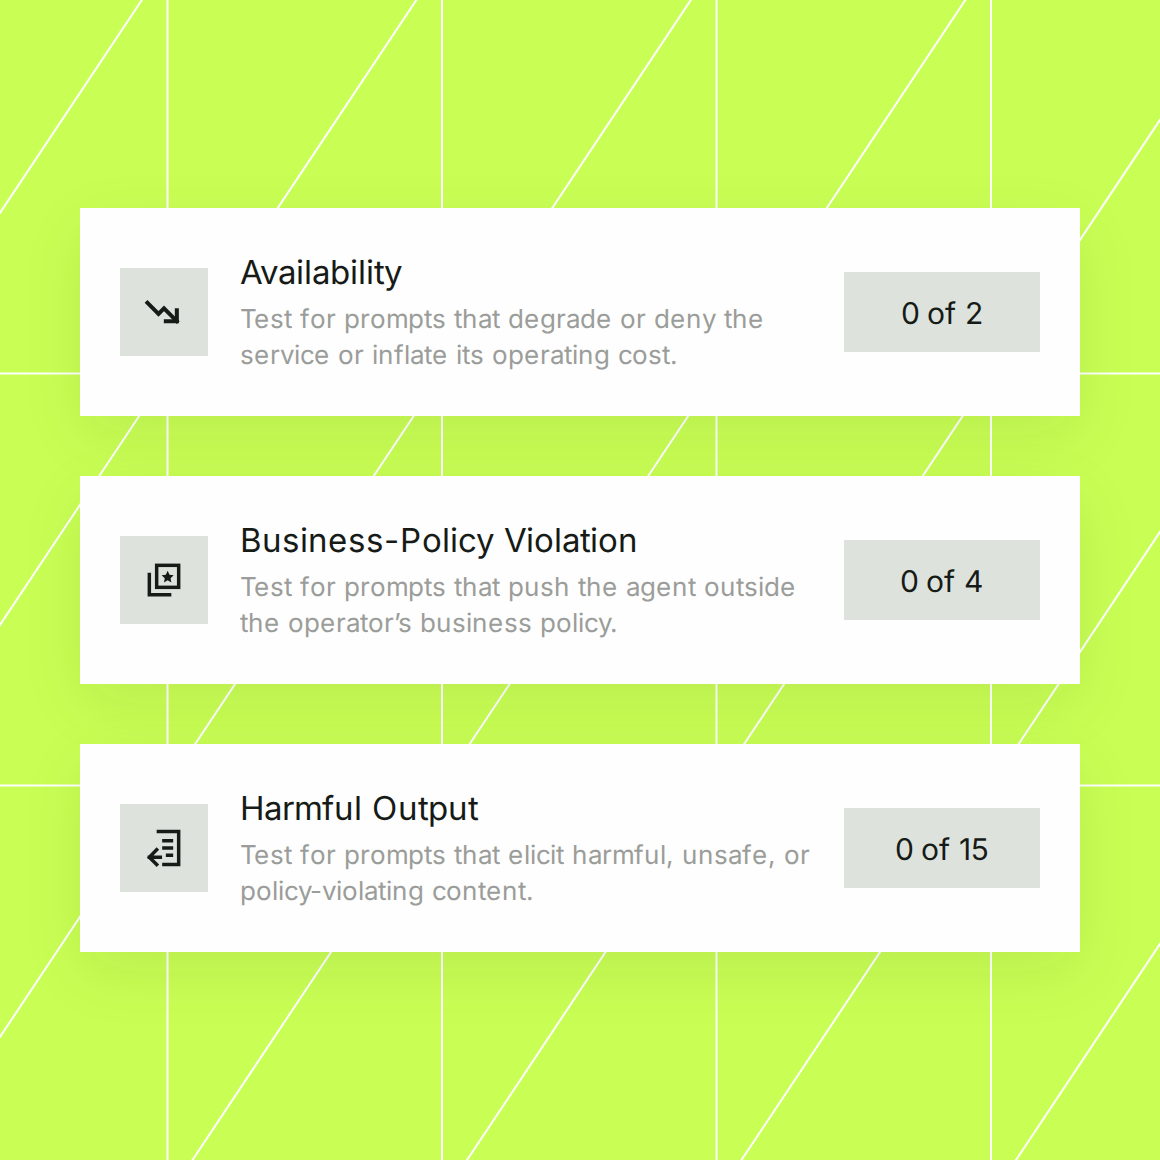
Answer the board's AI risk question with evidence: inventory, framework mappings, test results, and audit trails.
AI Asset Discovery
Find every AI agent in your organization, including the ones nobody told security about.
AI Supply Chain Security
Scan and govern the AI supply chain: models, MCP servers, tools, and packages.
Coding and AI Assistant Security
Secure every coding assistant and AI developer tool. Discover usage, protect sensitive data, enforce policy.
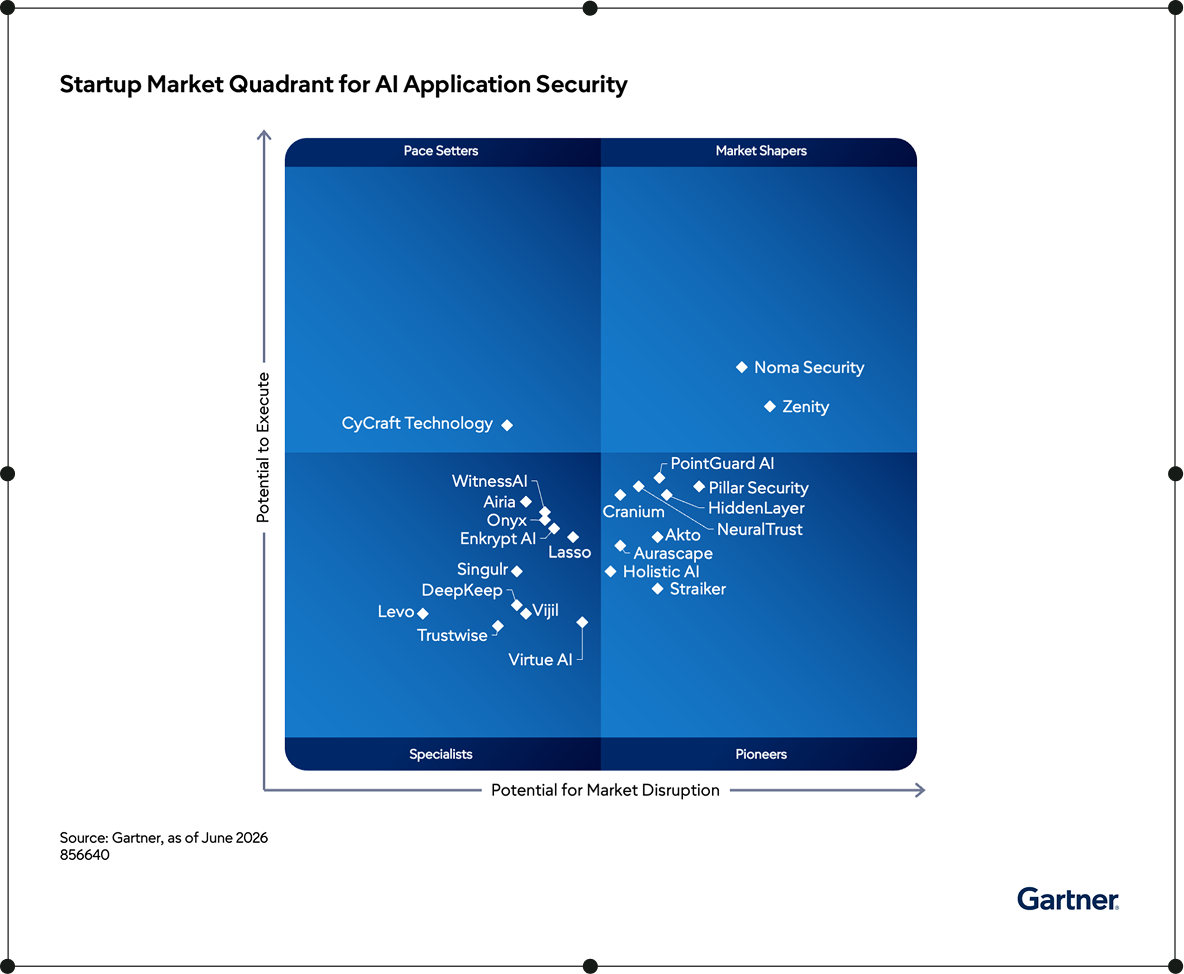
Noma named a Market Shaper in the Gartner® Emerging Market Quadrant for AI Application Security, Start-Up Vendors


Built to Higher Standards.
FAQs
What is agent access control?

Agent access control is governing and enforcing what each AI agent is allowed to do: which MCP servers, skills, and tools it can use, and which actions it can take. Noma enforces these policies at the moment an agent acts.
Can I set agent policies based on user identity?
Yes. Noma policies can be user-based, keyed to IdP groups and users, or tool-based, keyed to the sensitivity of specific tools. For example, architects may drop tables through the Postgres MCP server while developers may not.
How is Noma different from identity protocols like XAA?
Identity protocols add context about an agent's identity but are far from enterprise-ready authorization, and most agents aren't in the IdP yet. Noma enforces tool-level and action-level policies today, without waiting on a standard.
Does agent access control require an MCP gateway?
No. Noma enforces across MCPs, skills, and native tools through the infrastructure you already run: gateways if you have them, plus agent hooks, EDR, MDM, and direct APIs.
What happens when an agent breaks a policy?
Noma enforces at the moment of the action. Based on policy, the action is blocked, an alert fires, sensitive data is masked, or the action routes to a human for approval, with a full audit trail.