The Challenge
Employees across your organization are running agents on their machines, like Claude Cowork, Claude Code, and Codex. These agents have a growing ecosystem of MCP servers and skills that connect them to internal systems, cloud services, and sensitive data. As their autonomy grows, so does the risk, and the need for control.
Securing endpoint agents with Noma
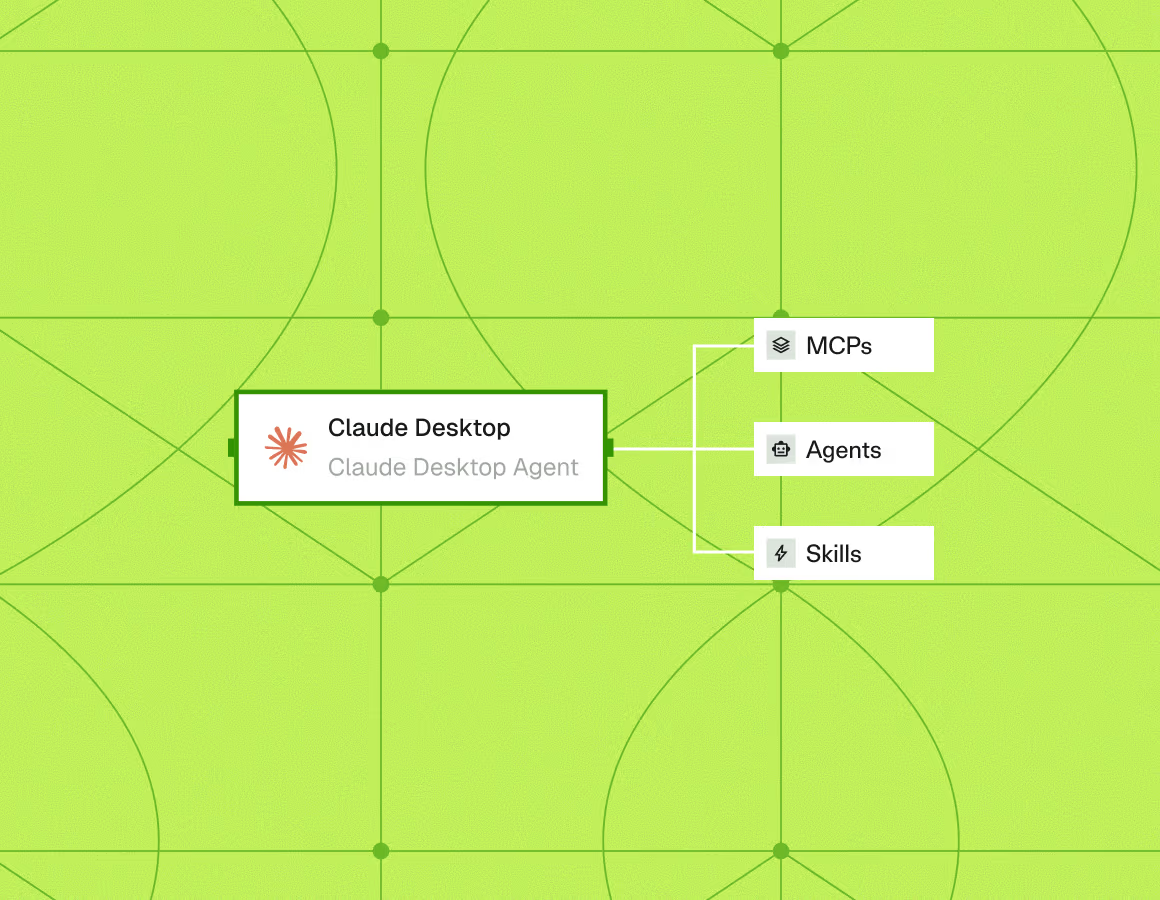
Find what employees have already connected
Noma discovers agents, MCP servers, and skills through your existing EDR or MDM. See where personal accounts and unapproved tools connect to company resources, without deploying another endpoint agent.
Stop risky behavior
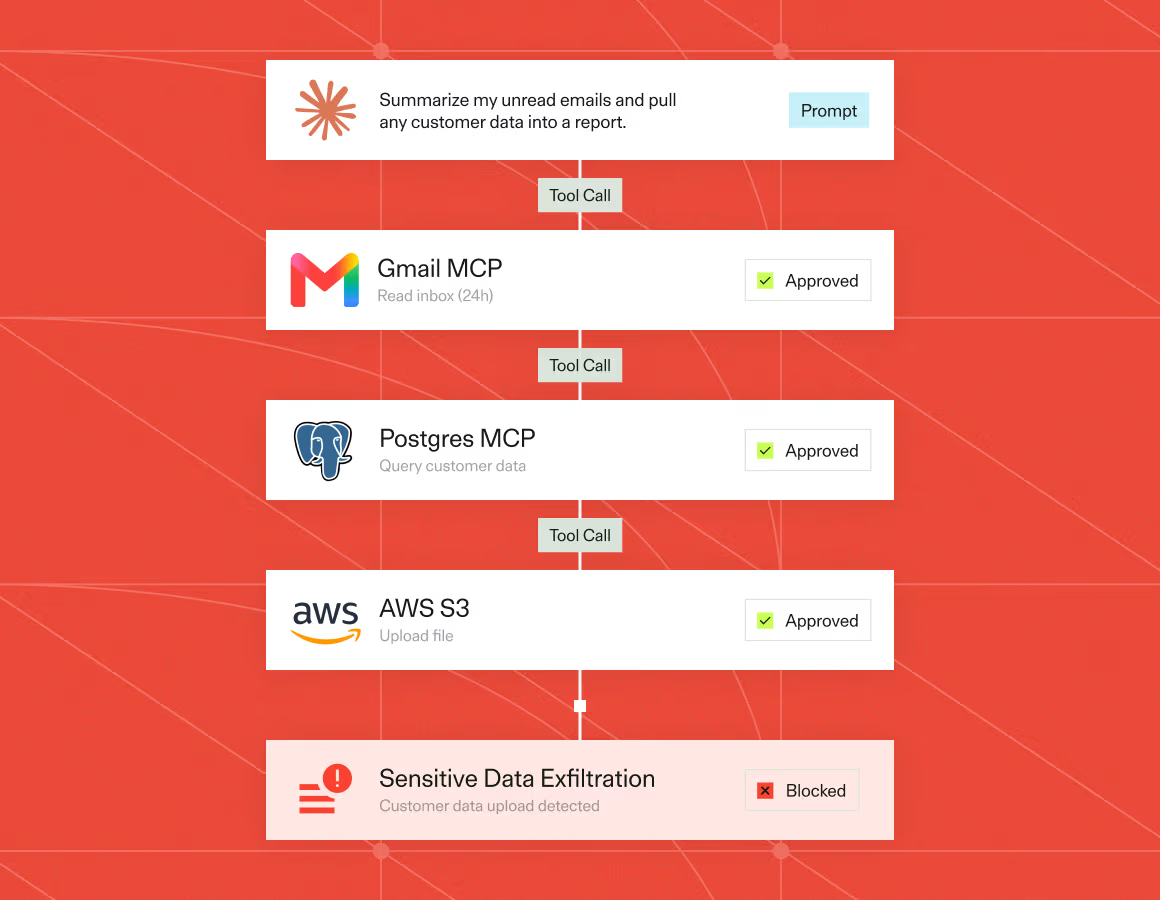
at runtime
Agents can go rogue or be manipulated, and even permitted actions can become destructive. Noma inspects each action with the context of the session, data access, identity, and behavior over time so you can stop risks without slowing down work.
Manage agent
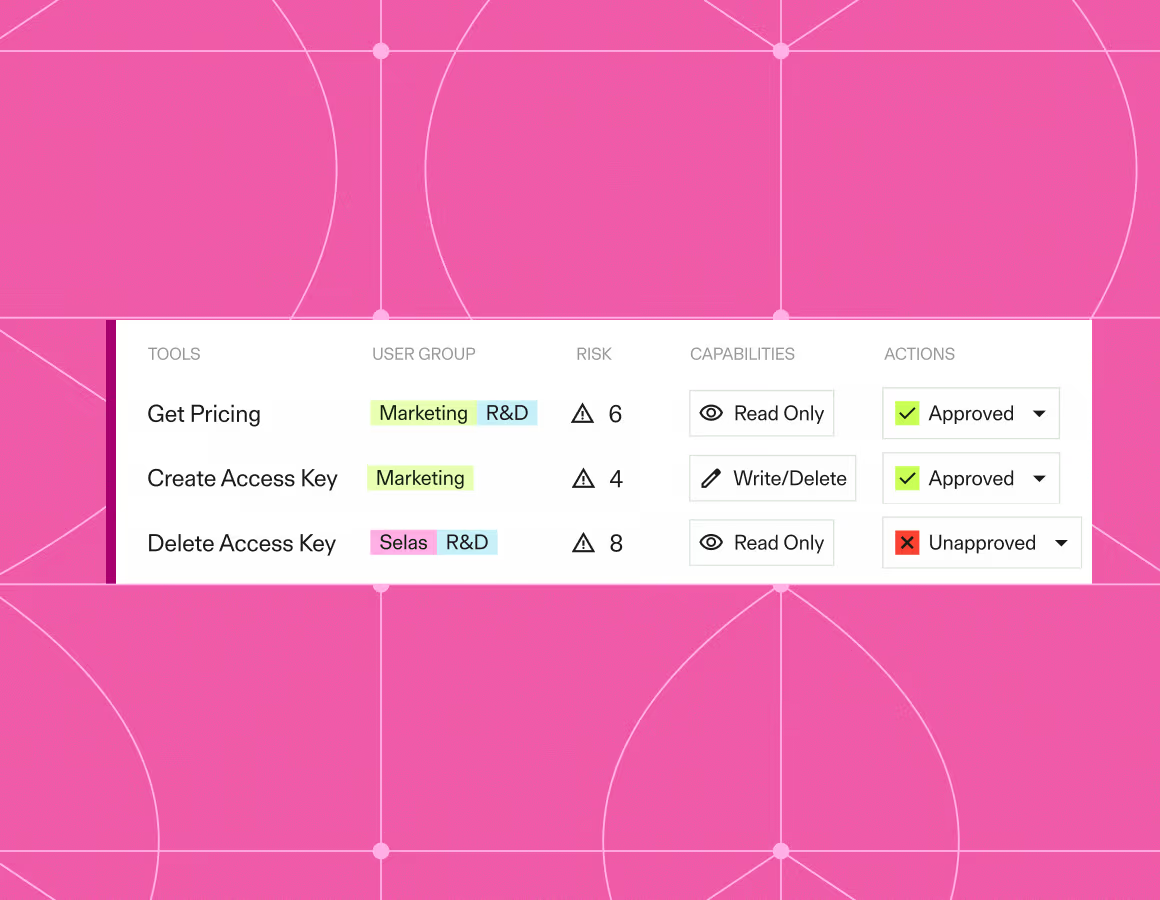
access and identity
Define which agents, skills, and MCPs are allowed, and what actions each agent can take based on owner identity or tool sensitivity. Then monitor agents in runtime to catch permitted actions that turn risky.
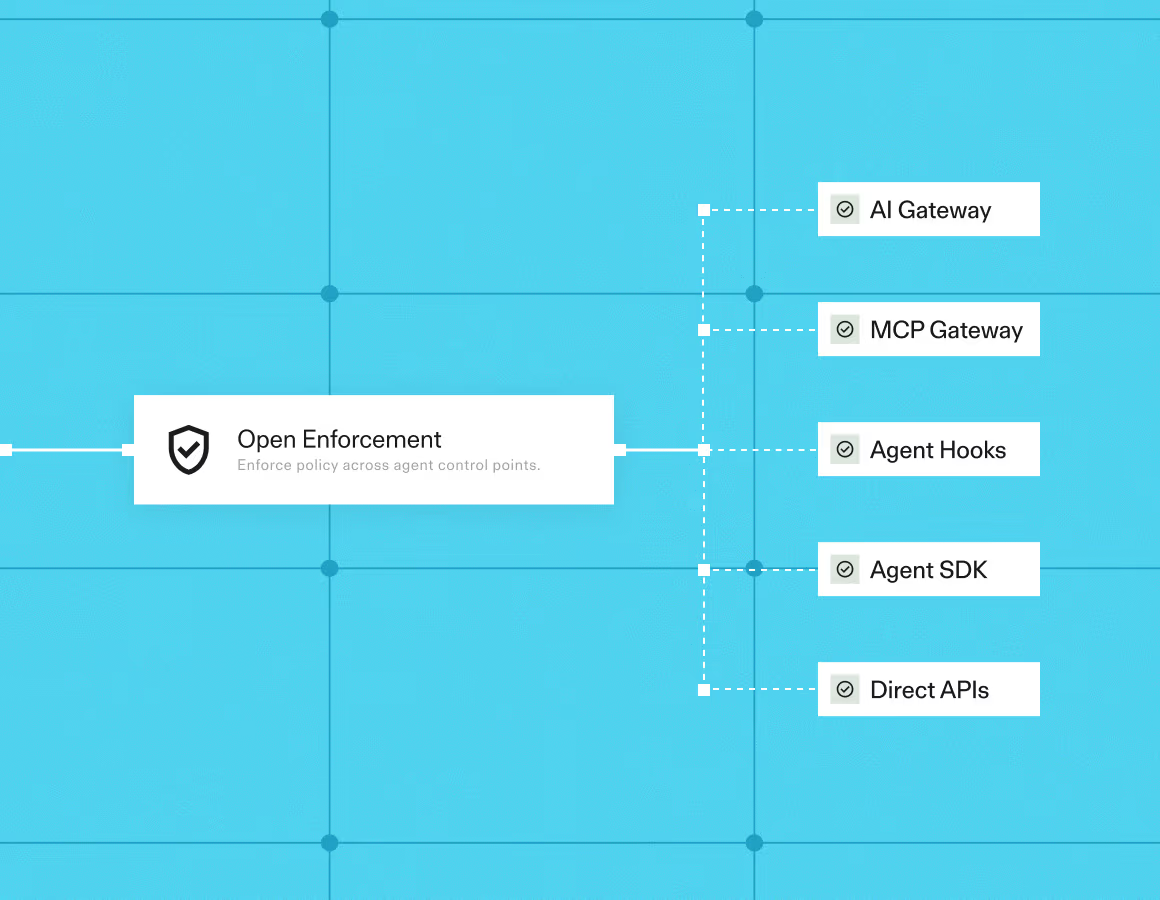
Keep policies consistent beyond the endpoint
Endpoint agents can run remote sessions and talk to other environments. Noma applies policies through hooks, gateways, and APIs, keeping control as work moves beyond the device.
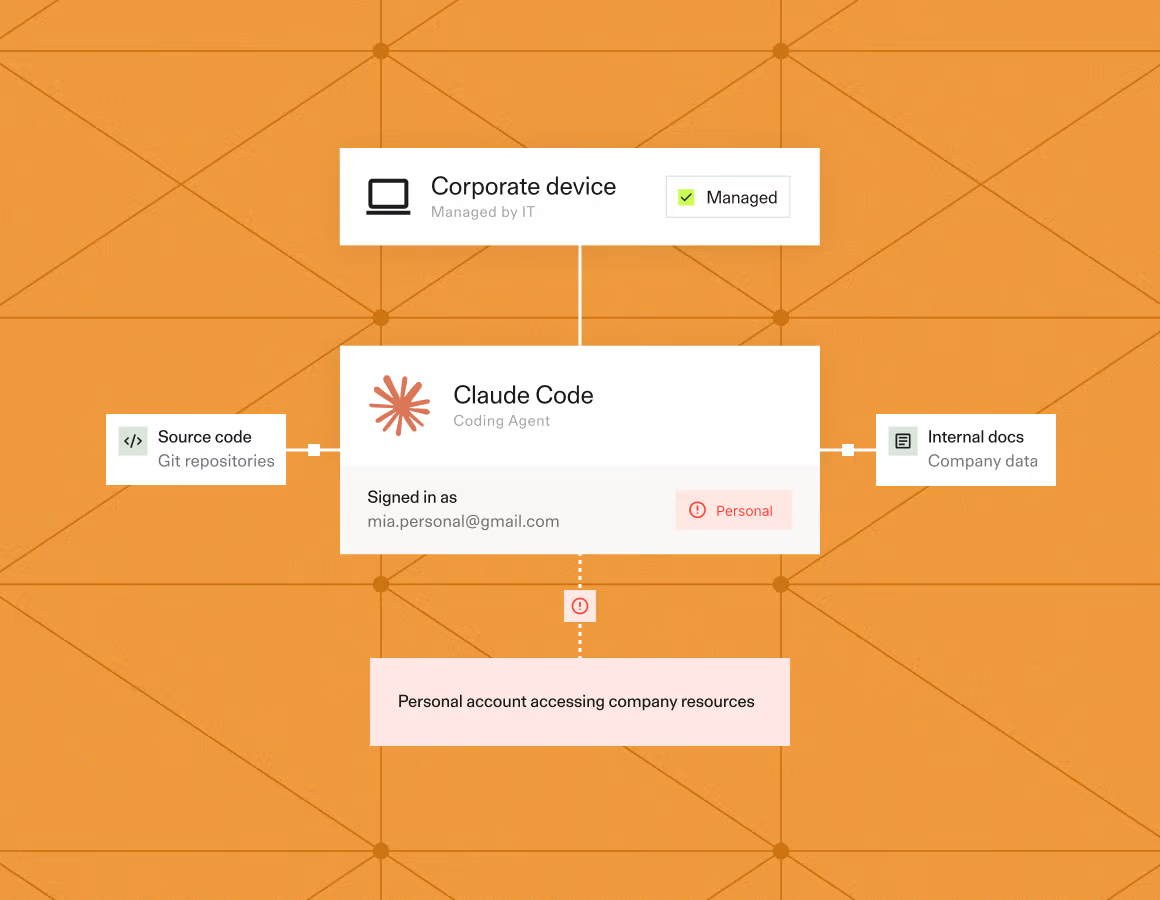
Find the agents running on personal accounts
See where agents use personal accounts to access company resources. Identify risky configurations so you can address them centrally.
Built to Higher Standards.
FAQs
What is endpoint AI agent security?

Endpoint AI agent security governs agents running on employee devices, including the tools they connect to and the actions they take. Noma combines discovery, access policies, and runtime protection for this activity.
How do you secure AI coding agents on employee devices?
Secure AI coding agents by discovering what employees run, limiting connected tools, and checking actions at runtime. Noma uses existing EDR or MDM for discovery and supported hooks, gateways, and APIs to enforce policy.
How can security teams find unapproved AI agents on endpoints?
Noma discovers AI agents, MCP servers, and skills on managed endpoints through your existing EDR or MDM. Security teams can identify unapproved tools and personal-account use, then review which company resources those agents can reach.
Can you restrict an AI agent’s tools without blocking the agent?
Noma Agent Access Control supports policies for specific tools and actions. You can approve an agent while restricting the MCP servers, skills, or operations it may use, so employees retain useful access within your policies.
Does endpoint AI discovery require another endpoint agent?
Noma uses your existing EDR or MDM to discover endpoint AI agents and connected components. Runtime enforcement uses supported agent hooks, gateways, and APIs, with the integration determined by how the agent operates.
How do you protect agent sessions that move from a device to the cloud?
Agent sessions can continue in the cloud after starting on an employee device. Noma applies policies to supported cloud sessions through hooks, gateways, and APIs, extending runtime protection beyond endpoint discovery.