Three AI environments. One security gap.
AI agents run in three distinct environments across your organization, each with a different architecture, different builders, and different risks.
01
RUN BY EMPLOYEES
Endpoint agents
Employees run coding and personal assistants on their machines, connecting them to MCPs and skills servers that reach into production code, internal APIs, and sensitive data. There's no approval process and very little visibility into what these agents are doing.
Noma for Endpoint Agents
02
BUILT BY ENGINEERING
Cloud agents
Engineering teams build AI applications on AWS Bedrock, Azure AI Foundry, Databricks, and in code with frameworks like LangChain and CrewAI. These carry the highest blast radius: customer-facing apps with access to sensitive data, agents chaining tool calls across production systems.
Noma for Cloud Agents
03
BUILT BY BUSINESS TEAMS
SaaS agent platforms
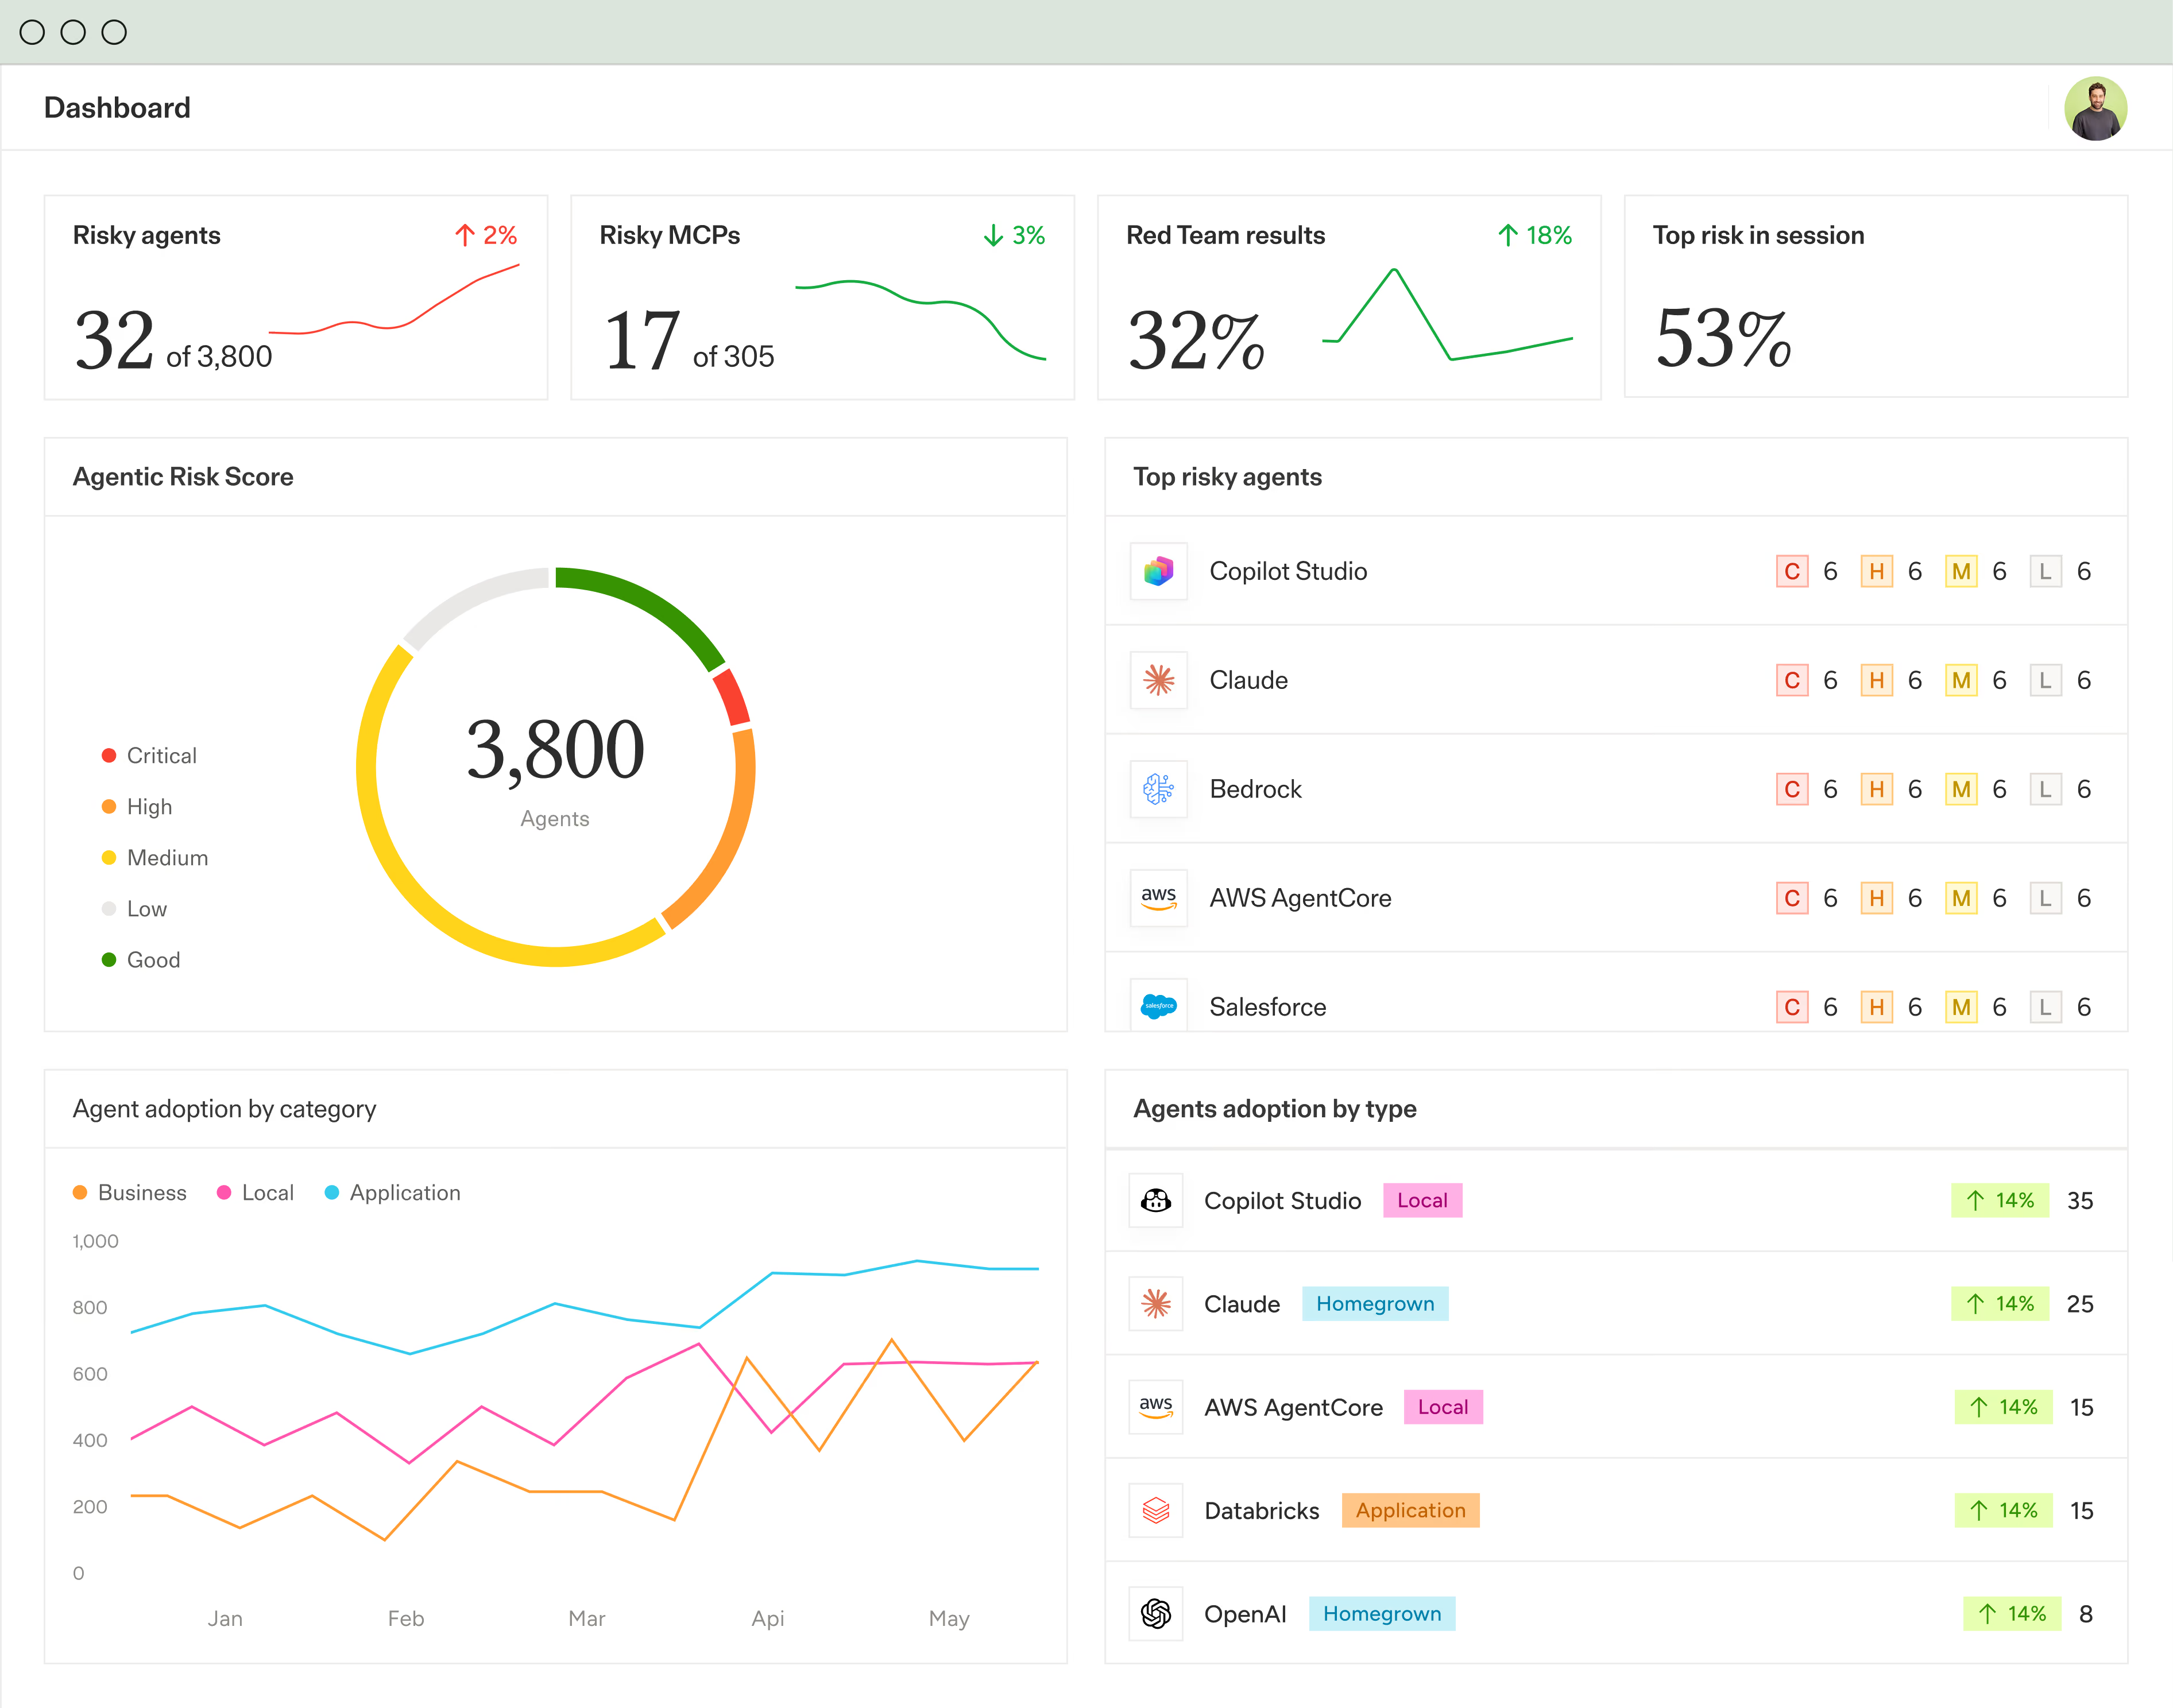
Business analysts, sales ops, HR, and finance teams build agents on Microsoft Copilot Studio, Salesforce Agentforce, and ServiceNow, often without telling security. Enterprises routinely discover 10 to 100x more agents than expected on these platforms.
Noma for SaaS Agent Platforms
Why Noma
Secure agents in every environment
Endpoint, SaaS, and cloud agents, all governed from one platform. No blind spots between environments.
Safely connect agents to sensitive systems
Noma understands the runtime context of every agent action so risky actions are avoided even when they seem legitimate.
Govern every agent risk in one place
Risky behavior, rogue agents, access and identity, business and operational risk. One agent control plane covers them all.
Enforce with the tools you already run
Noma enforces policy through your existing gateways, agent hooks, and AI stack. No new gateways, no re-architecting for security.
Four Products
That Share Intelligence
Use cases
Agent Runtime Security
Access control defines the boundaries. Behavioral detection enforces them. Both share context so enforcement is precise.
Learn More
MCP Security
Discover, assess, and govern every MCP server in your organization. Detect tool poisoning and supply chain attacks.
Learn More
Agentic Identity
Know who your agents are acting as, what they're allowed to do, and whether their actions match the user's intent.
Learn More
AI Asset Discovery
Find every AI agent running in your organization, including the ones nobody ever told security about. New agents are flagged the moment they appear.
Learn More
AI Agent Control Plane
A single governance layer that spans discovery, access control, and runtime enforcement across every AI surface.
Learn More
AI Supply Chain Security
Scan and govern your entire AI supply chain: models, MCP servers, tools, and packages you rely on. Every component gets a clear risk status.
Learn More
AI Compliance & Regulation
Answer the board's AI risk question with evidence: inventory, framework mappings, test results, and audit trails.
Learn More